Hackers altered temperature settings on blood plasma freezers used by France’s national blood service, the French Blood Establishment (EFS), pushing control setpoints from around −30°C to 110°C after targeting the company that maintains the cooling equipment. The incident took place overnight between November 1 and 2, 2026, and was detected by staff before it disrupted operations, according to France’s Health Ministry.
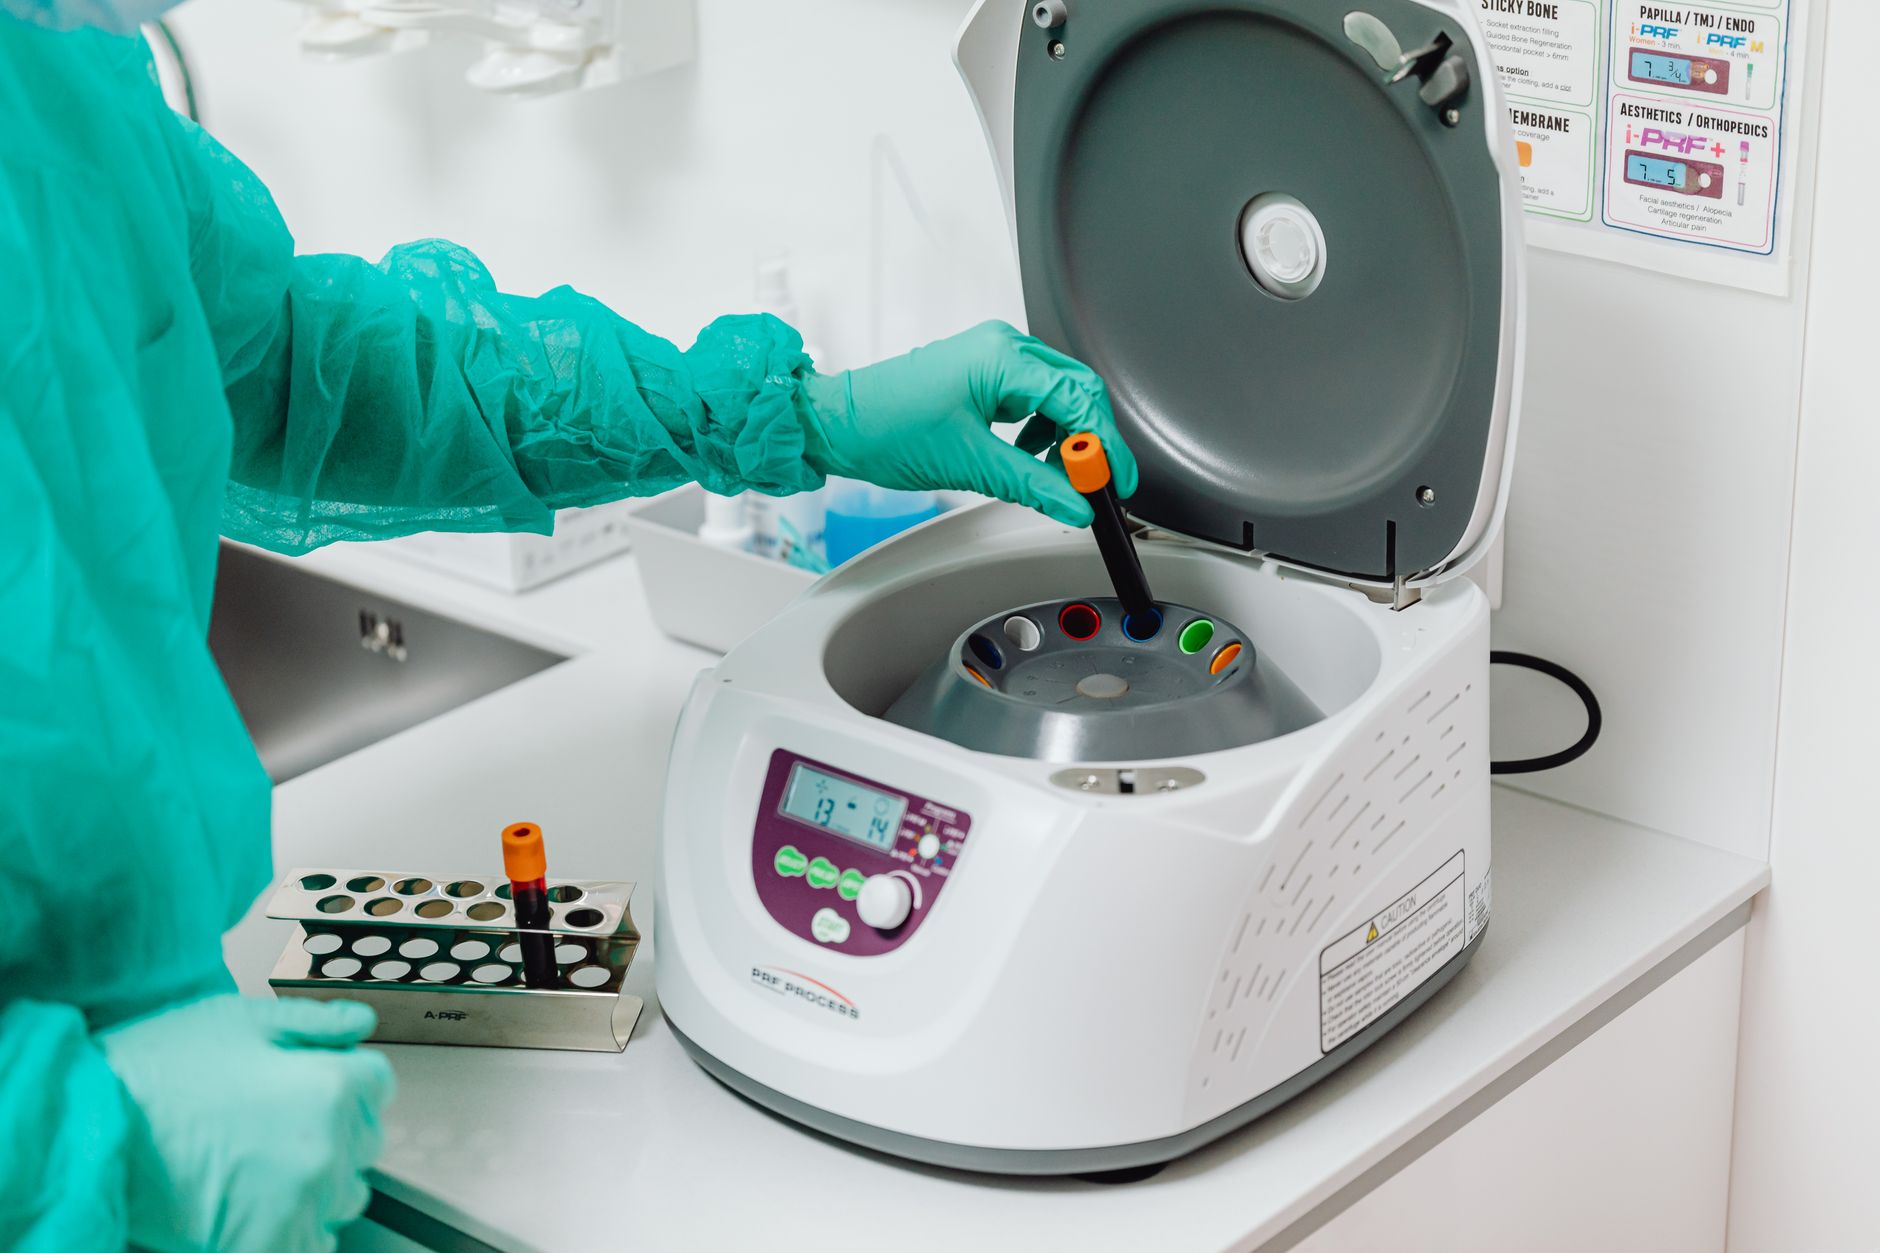
The attack reached EFS through Coolworld, a supplier of temperature-controlled equipment and maintenance services, including refrigerated containers used in medical settings. Cybersecurity News, citing reporting published by Cyberattaque that drew on Le Canard enchaîné, said facilities in Bourgogne-Franche-Comté were among those concerned.
An on-call technician caught the blood plasma freezers warming up
An on-call technician reportedly noticed temperatures rising during the night, which allowed teams to respond before the disruption affected operations. France’s Health Ministry said staff detected the abnormal temperatures in time and that the incident caused no operational consequences.
An account carried by the Ukrainian outlet Mezha, citing CNBC, described internal monitoring systems detecting increases in temperature thresholds at refrigeration units across three EFS facilities. In that account, staff managed to transfer the supplies to secure refrigerators in time, preventing the plasma from spoiling, and no samples were lost.
Initial information concerned donor samples retained for blood safety monitoring. EFS later told Le Canard enchaîné that frozen plasma intended for transfusions was also involved. No destroyed plasma, disrupted transfusions or harm to patients has been confirmed, and no theft of donor information has been reported.
Why the 110°C figure needs careful reading
The reported 110°C number describes a setpoint — the temperature requested through a control system — and does not establish that freezer interiors, blood samples or plasma bags reached that temperature, Cybersecurity News noted. Controller settings, measured air temperatures and temperatures inside stored products are separate readings.
That distinction matters because the risk depends on actual storage conditions and how long products sat outside approved limits. Reporting on the incident notes that fresh frozen plasma requires storage at −25°C or below, and that a prolonged temperature rise could make affected supplies unsuitable for transfusion.
Key details remain undisclosed: the number of affected units, the length of the disruption, and the temperatures actually reached inside stored products. No public technical findings identify the attackers or explain how they entered Coolworld’s systems.
France’s health ministry and cyber agency are investigating
According to EFS, the cyberattack targeted the systems of a contractor responsible for maintaining the refrigeration equipment. The French Ministry of Health and the country’s national cybersecurity agency are investigating the circumstances of the incident, Mezha reported.
Investigators have not publicly identified a controller model, an exploited vulnerability or a stolen maintenance account. Cybersecurity News cautioned that claims attributing the incident to a specific Danfoss flaw would go beyond the available evidence.
A wider wave of attacks on European refrigeration systems
The episode follows earlier attacks against supermarket refrigeration systems, where attackers reportedly changed settings to force continuous defrosting. Cybersecurity News stressed that similar behavior does not prove the same attackers, equipment or entry method were involved at Coolworld.
Mezha’s account tracks that wave in more detail. The first attacks on refrigeration systems in Europe were recorded on October 12, when supermarkets in France, Belgium and the Netherlands saw units driven into continuous defrost cycles at temperatures of 50°C. In early November, hackers raised refrigeration temperatures in Sweden, Belgium and Luxembourg, and reports have since put the spread at more than 11 countries. In Italy, around 20 retail outlets were affected, and four of Coop’s 300 supermarkets in Sicily had to discard all their food.
Cybersecurity analysts had previously warned that roughly 13,000 refrigeration systems across Europe run outdated software affected by known vulnerabilities.
Claimed responsibility that cannot be verified
The attackers’ identities and motives have not been officially established. Cybernews reported that the Russian hacking groups NoName057(16) and Z-Pentest had claimed responsibility, according to Mezha. NoName057(16) published a sample database containing more than 2,500 rows of login credentials and passwords belonging to employees and customers of Danfoss, a manufacturer of refrigeration equipment. The groups’ Telegram posts were later deleted, and their involvement in the breach cannot currently be independently verified.
“The problem isn’t ‘evil hackers’ but the systemic negligence of European and American operators who have ignored basic cybersecurity requirements for years,” the Z-Pentest group wrote.
CERT-FR guidance on Danfoss controllers and exposed interfaces
An October 12 security alert from CERT-FR confirmed numerous compromises involving Danfoss AK-SM and AK-SC controllers, alongside Copeland and Dixell XWEB systems. The agency warned operators against exposing management interfaces directly to the internet.
CERT-FR’s recommendations include:
- removing public internet access to control systems;
- reviewing full device configurations and checking defrost schedules;
- restoring remote access only through secure VPNs or protected networks;
- applying firmware updates to supported equipment;
- changing default passwords and enabling applicable security settings.
Cybersecurity News also documented internet-facing Danfoss systems, while noting that search results alone do not establish whether individual devices are vulnerable or compromised. No public evidence connects those exposed systems to the EFS incident.
For healthcare providers, Cybersecurity News wrote, the reported incident highlights risks extending beyond stolen records, because a supplier compromise can affect equipment that preserves essential medical products. Independent temperature monitoring and prompt staff response were important safeguards in the case of the blood plasma freezers, although the full technical cause remains unknown.
Pressure on blood supplies has drawn attention elsewhere this year, including the Red Cross declaration of a second-ever national blood crisis. For other recent developments in France, see our report on the French Senate bill making protesters pay damages.